Pipeline Hijacking! An Offensive Perspective on CI/CD and the Hunt for Credentials
How attackers steal credentials from a CI/CD runner, and how to shut them out with OIDC, SHA pinning and admission-time verification.
2 posts with this tag
How attackers steal credentials from a CI/CD runner, and how to shut them out with OIDC, SHA pinning and admission-time verification.
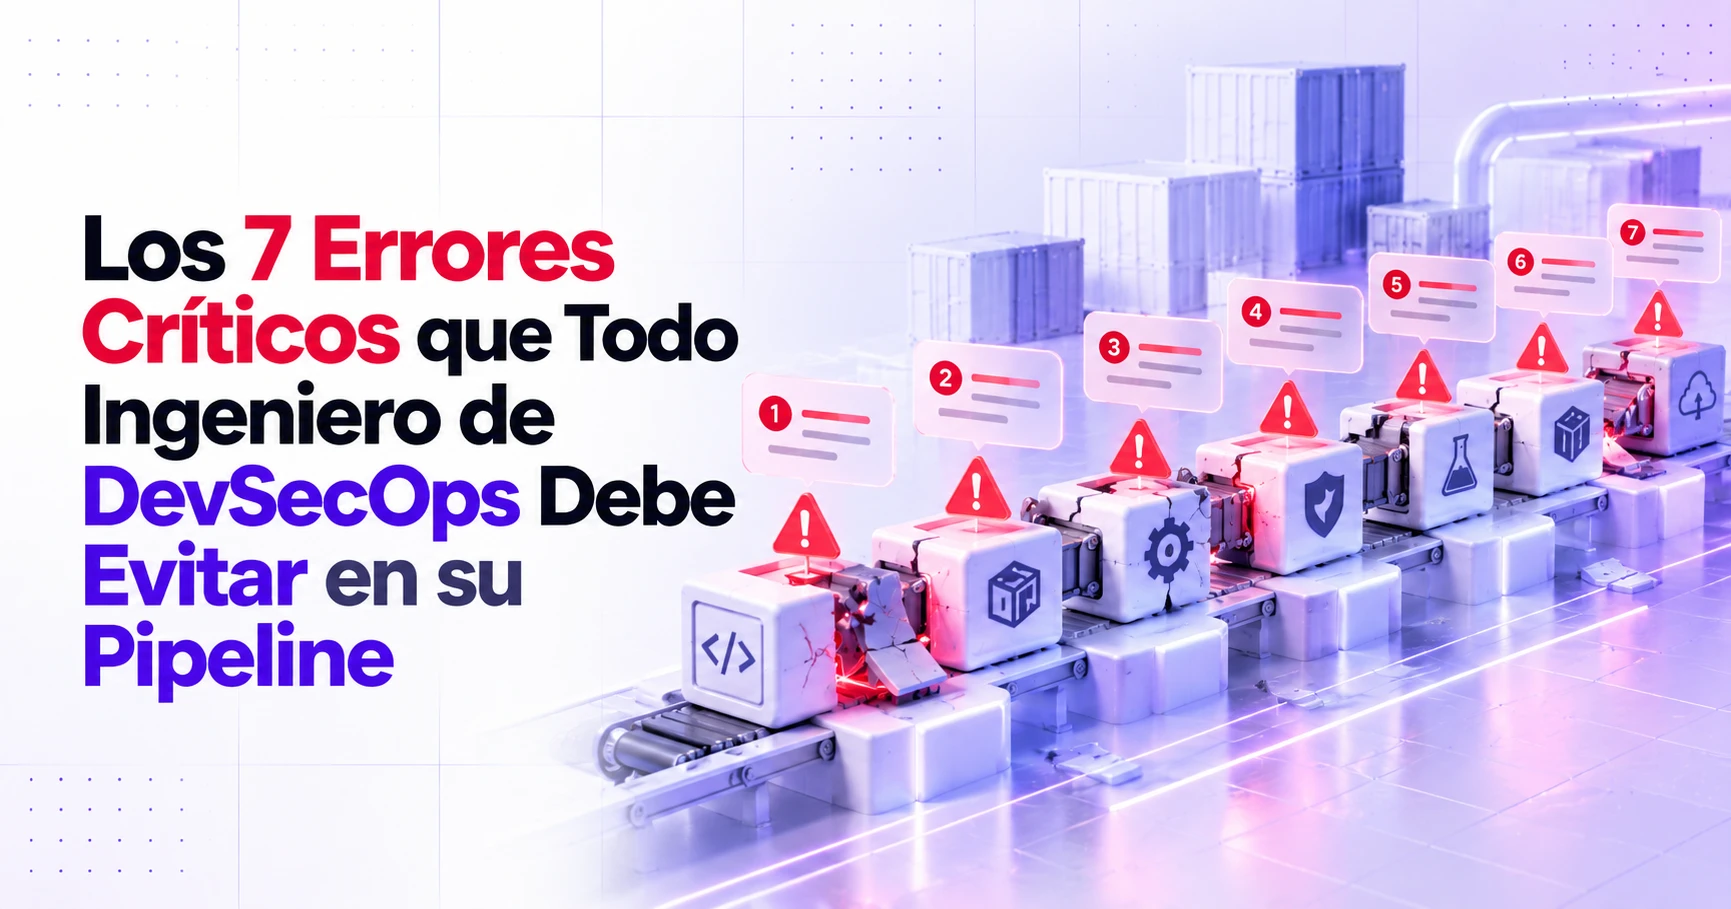
Seven pipeline mistakes and their fixes: Semgrep on the PR, a Snyk gate, CVSS with EPSS and KEV, pinned Actions, gitleaks, OIDC and ZAP in staging.